
HIPAA Compliant Digital Marketing Examples: What is the principle of minimum necessary in relation to PHI?
In digital marketing, the Minimum Necessary Standard is a HIPAA Privacy Rule requirement that mandates covered entities and business associates to use, disclose, or request only the smallest amount of Protected Health Information (PHI) needed to accomplish a specific marketing goal. Rather than providing a one-size-fits-all list of “allowed” data, HIPAA requires organizations to make “reasonable efforts” to calibrate their data usage based on the specific context of the campaign.
Does VaultDocSites employ the principle of minimum necessary in relation to PHI?
Yes, VaultDocSites frameworks provided by PatientGain employ the HIPAA minimum necessary standard and related technical controls to limit access to Protected Health Information (PHI).
How VaultDocSites Implements Minimum Necessary and HIPAA Compliance
- Role-Based Dashboards: VaultDocSites provides a HIPAA Compliant Dashboard for front desk staff and clinic personnel, restricting internal view access so users only see the data fields and patient inquiries necessary for their specific administrative roles.
- Secure Data Transmission: Instead of exposing raw data or using unencrypted channels, the infrastructure limits data collection on web forms to what is required for appointment booking or patient communication, adhering to data minimization principles.
- Business Associate Agreement (BAA): PatientGain supports compliance by executing a comprehensive BAA with the healthcare practice, establishing legal accountability for handling PHI according to permitted limits.
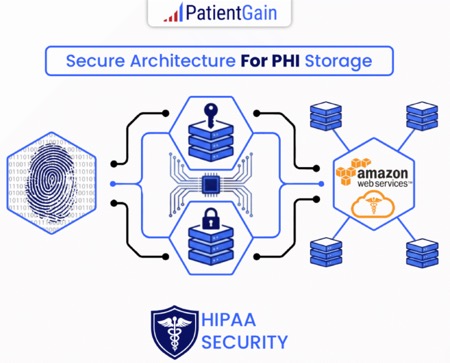
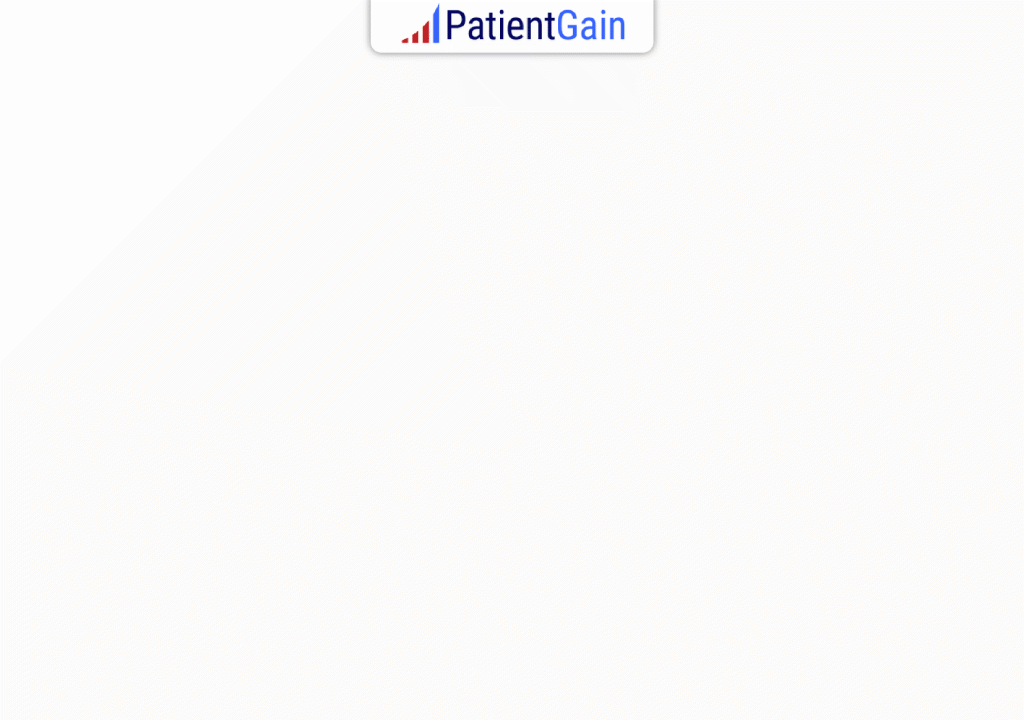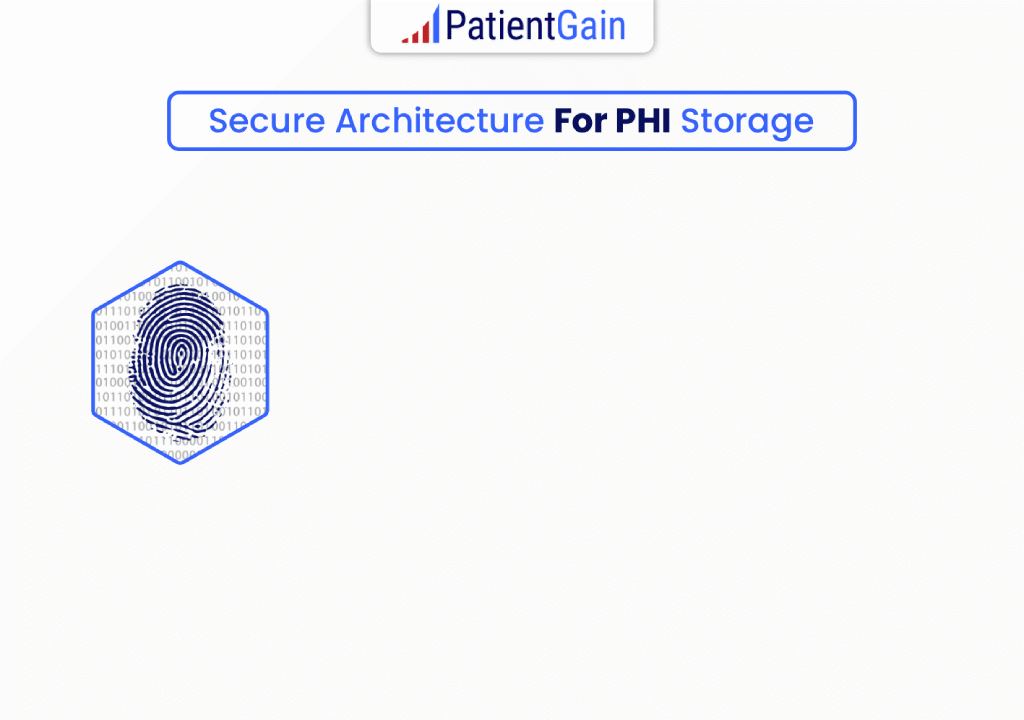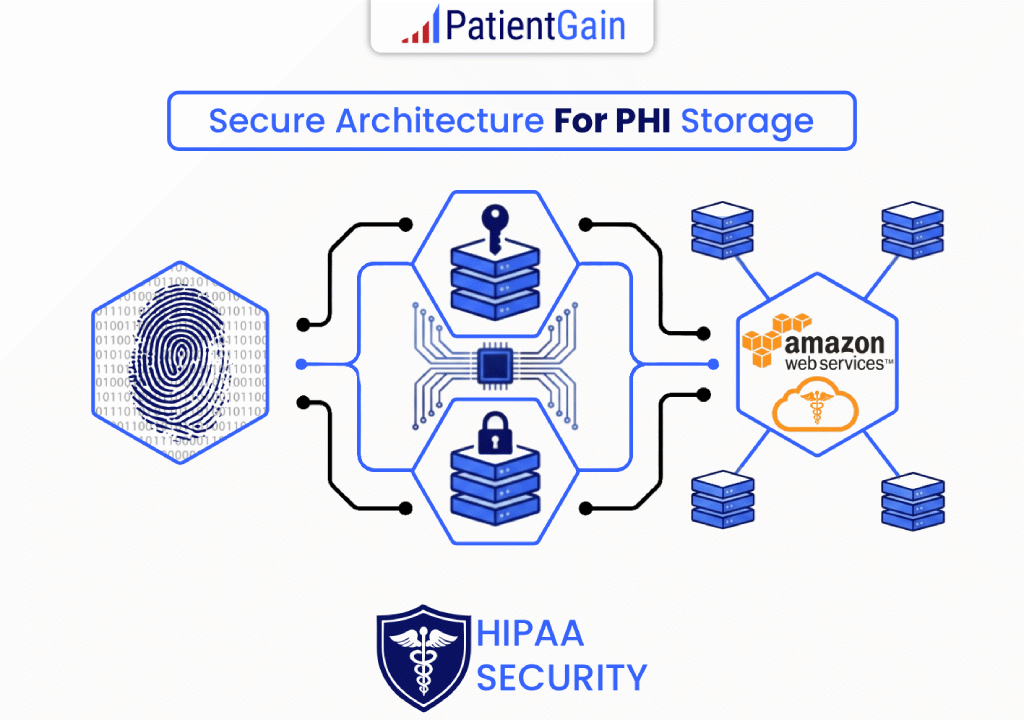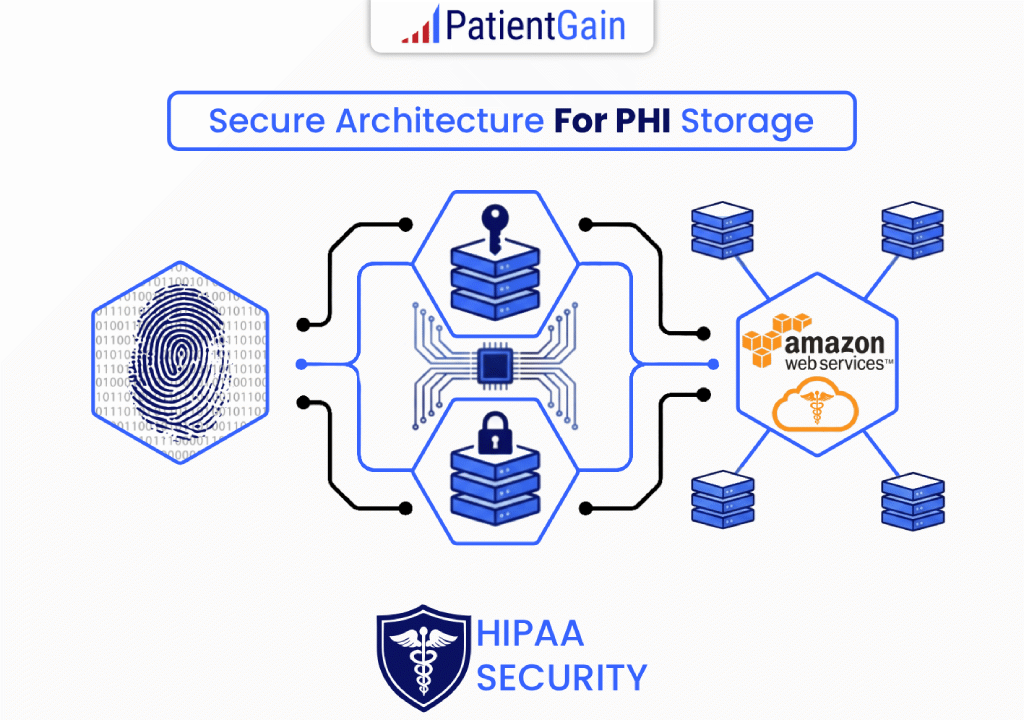
- Infrastructure Security: Hosted on enterprise-grade cloud environments like Google Cloud Platform or AWS, the platform uses technical safeguards to prevent unauthorized broad access to stored web inquiries or patient data.
Key Principles in Digital Marketing
- Purpose Specificity: Before launching a campaign, you must define exactly why PHI is needed. If the goal is a general newsletter, no PHI (like specific diagnoses) should be used.
- Least Privilege: Access to patient data within marketing tools should be role-based. For example, a graphic designer needs access to stock photos, but not the patient’s medical history or billing details.
- Data Minimization: When segmenting audiences, use the narrowest range of data possible. Instead of exporting a full patient list, use only the essential identifiers (like an email address) required for the delivery of the message.
Examples of the Principle in Action
| Marketing Activity | Non-Compliant (Excessive) | Compliant (Minimum Necessary) |
|---|---|---|
| Email Reminders | Including the specific treatment or diagnosis in the subject line (e.g., “Time for your HIV follow-up”). | Using a generic subject line (e.g., “Upcoming Appointment Reminder”) and keeping sensitive details inside a secure portal. |
| Vendor Sharing | Sending a marketing agency a spreadsheet with full medical histories to “help with targeting”. | Sharing only a de-identified list of zip codes or a limited dataset authorized for a specific campaign. |
| Website Analytics | Using tracking pixels on patient portal login pages that capture IP addresses and specific medical queries. | Configuring pixels to fire only on general health-education pages and disabling them on pages where PHI is entered. |
Important Exceptions
The minimum necessary standard does not apply in these specific marketing-related scenarios:
- Valid Authorizations: If a patient signs a specific, written HIPAA authorization for marketing, you may use the information exactly as specified in that form.
- Disclosures to the Individual: When a patient requests their own records via a marketing portal, the full record must be provided without limitation
 Send Text
 How may I help you?